
RFID Casino Chip Security: Encryption Standards and Data Protection for Gaming Operations
- By admin
- Uncategorized
- 0 Comments
- Haziran 29, 2025
Casino chips are more than game tokens—they are high-value financial instruments that circulate in an environment where security breaches can result in substantial losses. RFID technology has transformed chip management by embedding digital identity into each chip, enabling automated tracking and validation. However, this digital identity introduces a new security dimension: the data carried by each chip’s transponder must be protected against interception, cloning, and manipulation. Encryption standards and data protection protocols are the backbone of RFID casino chip security, and understanding their design, implementation, and regulatory implications is essential for any property deploying RFID-enabled table game operations.
The Security Landscape for RFID Casino Chips
RFID casino chips operate in a uniquely challenging security environment. Unlike retail inventory tags or access control badges, casino chips:
– Represent direct monetary value: Each chip’s denomination corresponds to a specific cash equivalent, making the data embedded in the transponder functionally equivalent to currency.
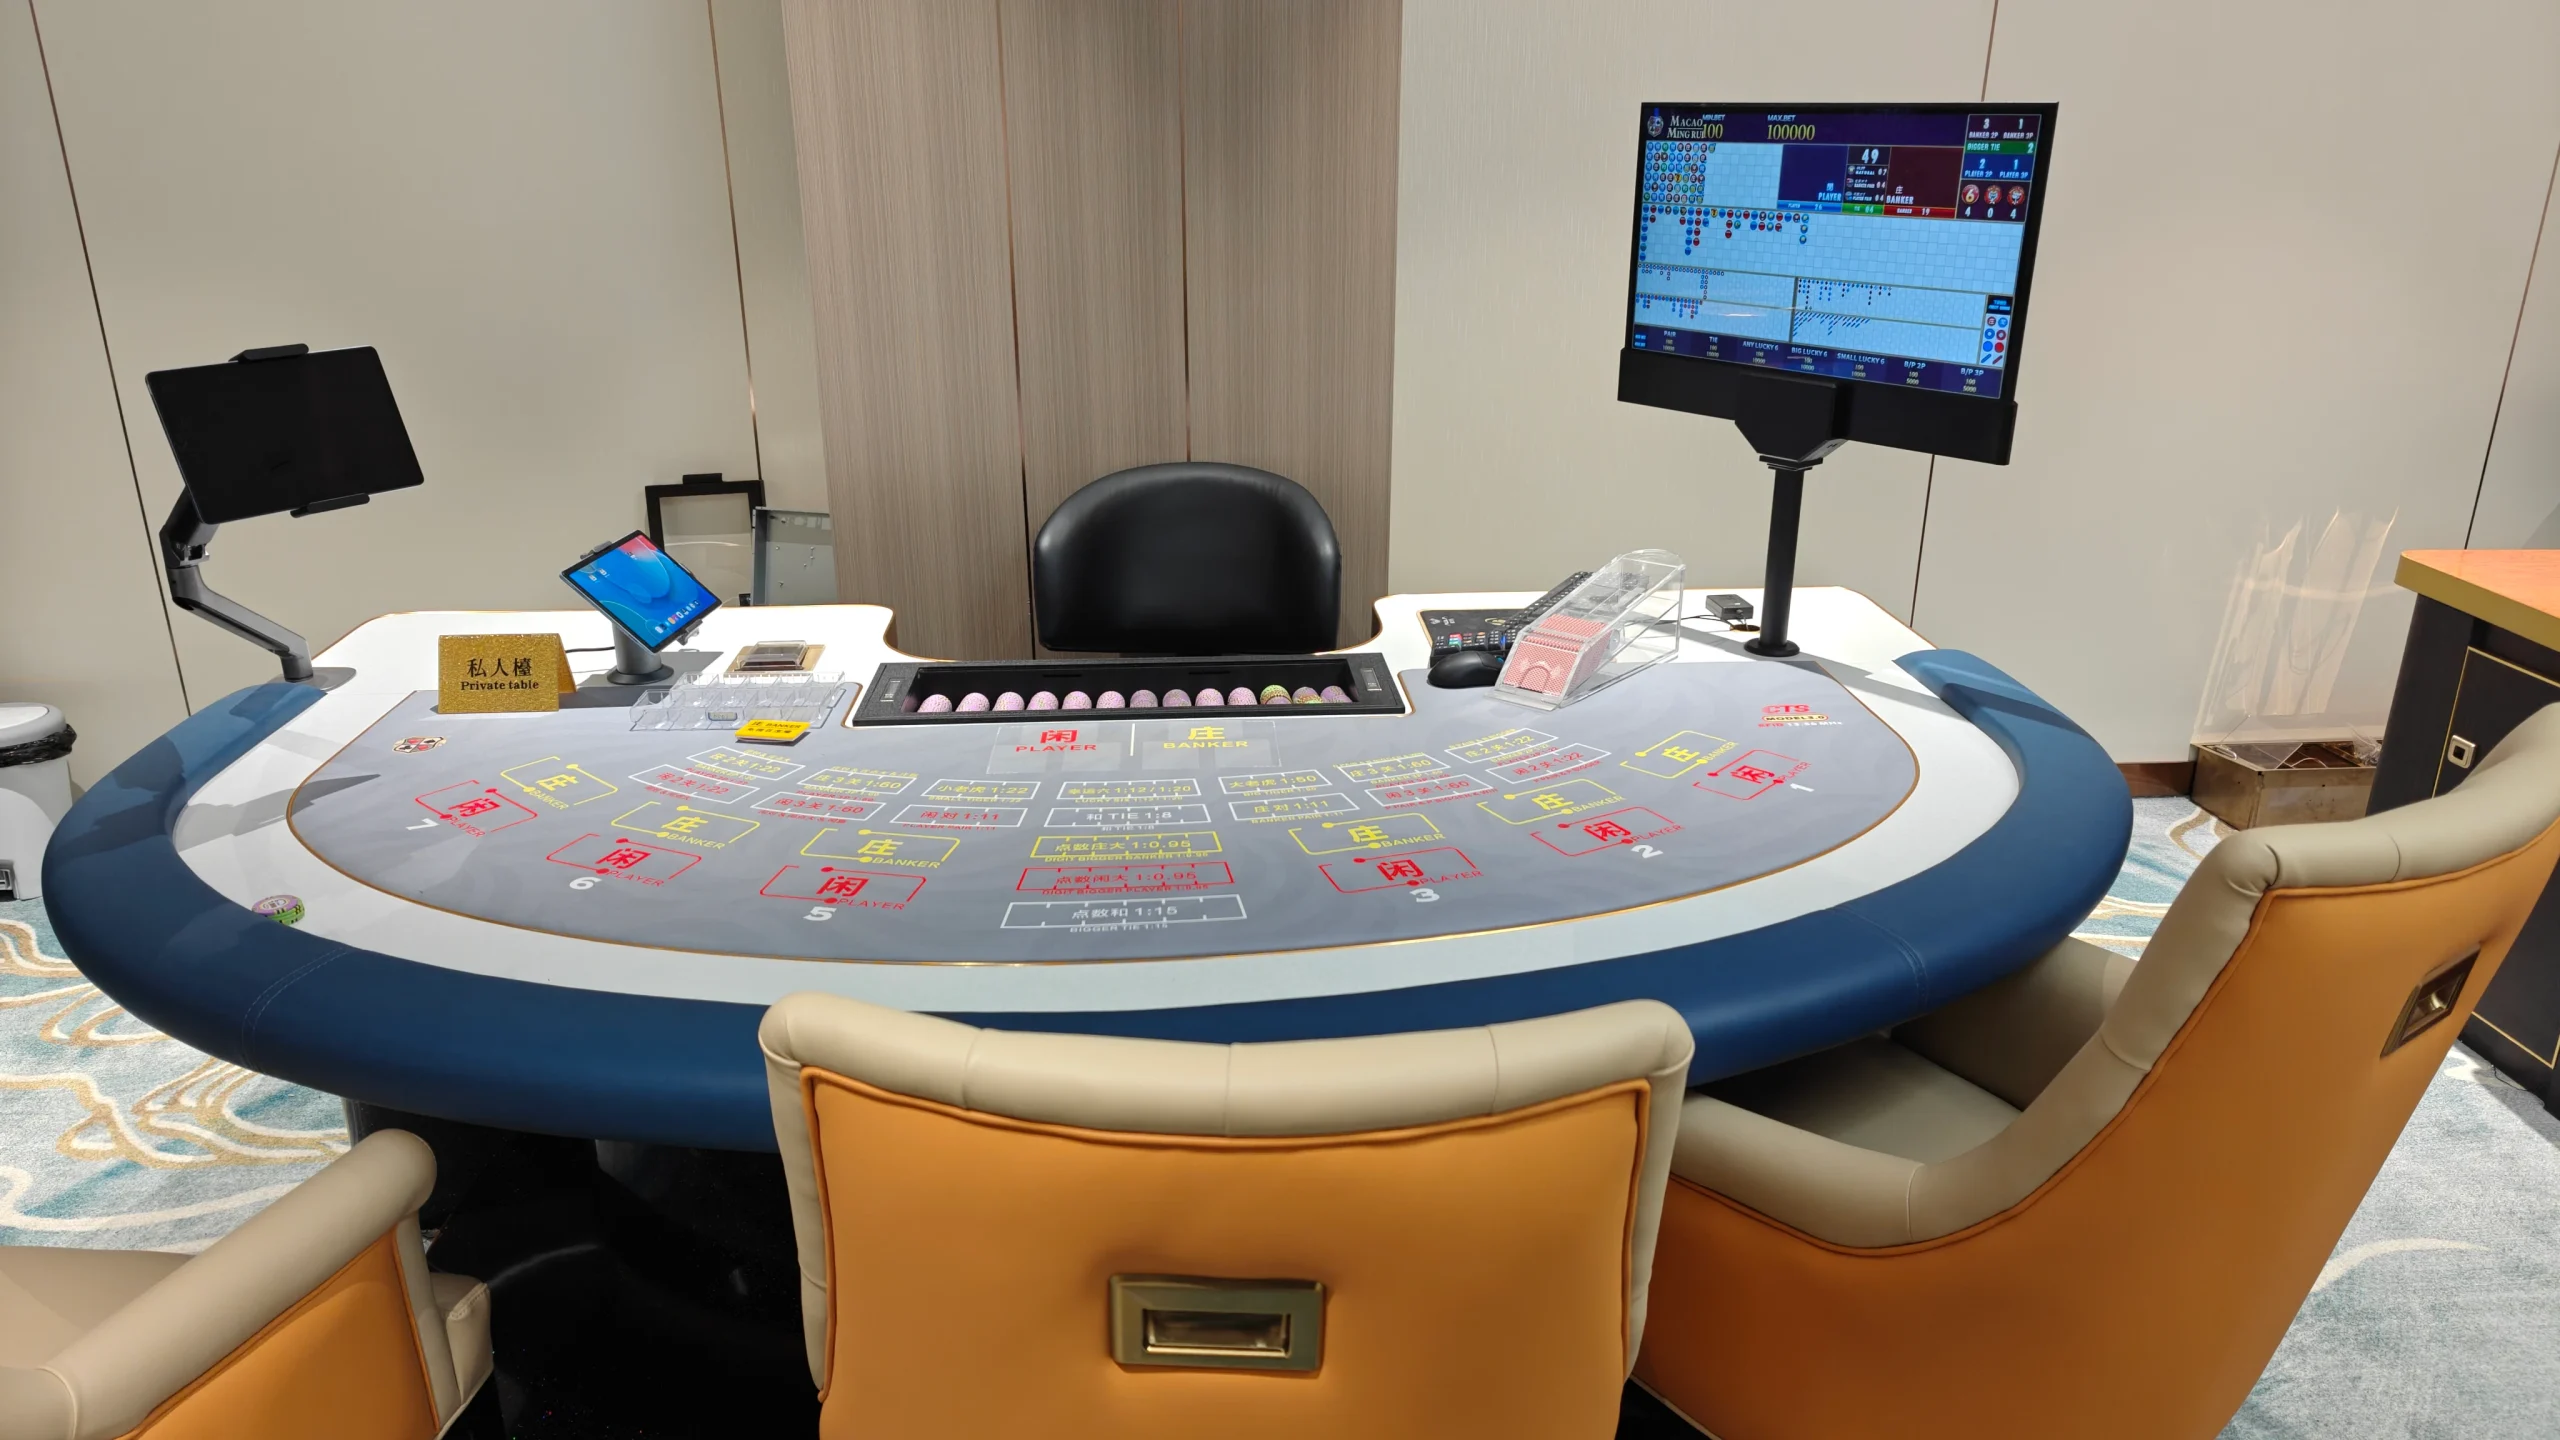
– Circulate in public spaces: Chips are handled by players, dealers, and staff in open areas where unauthorized parties may attempt to intercept or manipulate RFID signals.
– Must withstand sustained physical wear: Casino chips endure years of handling, impact, and environmental exposure while maintaining both physical integrity and transponder functionality, including cryptographic performance.
– Are subject to regulatory oversight: Gaming authorities require that chip security measures meet defined standards, and failure to maintain adequate protections can result in compliance violations and operational penalties.
These conditions demand a security framework that addresses multiple threat vectors simultaneously: external attack from sophisticated counterfeiters, signal interception by unauthorized readers, data manipulation through protocol exploitation, and insider threats from personnel with access to chip management systems.
Encryption Architecture for RFID Casino Chip Transponders
The encryption architecture embedded in casino chip transponders follows a layered design that protects data at rest (stored on the chip) and data in transit (communicated between chip and reader):
Transponder Data Encryption
Each chip’s transponder stores several data elements: a unique identifier, denomination data, issuance metadata, and authentication markers. These elements are encrypted using algorithms selected for their resilience against known attack methods while remaining computationally feasible for the chip’s embedded processor to execute within read-time constraints.
Symmetric key encryption: Many casino RFID implementations use symmetric key algorithms—where the same key is used for encryption and decryption—to protect stored data on the transponder. The key is stored within the chip’s secure memory area, accessible only to the chip’s internal cryptographic processor. This approach balances security strength with the processing speed required for rapid read cycles during live table operations.
Asymmetric key elements: Some implementations incorporate asymmetric cryptography—using paired public and private keys—for specific authentication functions. When a reader initiates a challenge-response sequence, the chip may use its private key to sign a response that the reader verifies using the corresponding public key stored in the system database. This method provides strong authentication without requiring the reader to possess the chip’s secret key material.
Key diversification: Rather than using a single encryption key across all chips, leading systems employ key diversification algorithms that generate unique keys for each chip based on its serial number and a master secret. This approach ensures that compromising one chip’s key does not expose the entire chip set, as each chip’s encryption key is mathematically independent of others in the inventory.
Challenge-Response Authentication Protocols
Static data on a transponder—even encrypted data—can potentially be captured and replayed by unauthorized readers. Challenge-response protocols prevent this vulnerability by requiring dynamic interaction between reader and chip during every read event:
Reader challenge generation: When a table reader initiates a chip read, it generates a random challenge value—a cryptographic nonce—that is unique to that specific read event. This nonce is transmitted to the chip as part of the read request.
Chip response computation: The chip’s embedded processor uses its internal key material and the received nonce to compute a response value, typically through a keyed hash function or an encryption operation that incorporates the nonce. The response is transmitted back to the reader.
Reader verification: The reader (or its associated processing unit) uses the chip’s known key material—retrieved from the system database—and the same nonce to compute the expected response. If the chip’s response matches the expected value, the read is authenticated. If the values do not match, the chip is flagged as potentially compromised.
Because each read event uses a unique nonce, captured response data from a previous read cannot be reused by an attacker attempting to impersonate a legitimate chip. This dynamic authentication layer prevents replay attacks, which are among the most common threats to RFID-based financial instruments.
Mutual Authentication Between Chip and Reader
Advanced casino RFID systems implement mutual authentication, where both the chip and the reader verify each other’s legitimacy before exchanging data:
Chip authenticates the reader: Before responding to a read request, the chip verifies that the requesting reader is authorized to communicate with casino chip transponders. This verification prevents unauthorized readers from extracting data from chips, even if the unauthorized reader can generate valid-looking challenge values.
Reader authenticates the chip: As described above, the reader verifies the chip’s response to confirm that the transponder carries legitimate data and is not a cloned or counterfeit device.
Session key establishment: After mutual authentication succeeds, the chip and reader may establish a temporary session key used to encrypt subsequent data exchanges within that read cycle. This session key is derived from the authentication process and is discarded after the read event concludes, preventing any retrospective decryption of intercepted communications.
Data Protection in the System Infrastructure
Transponder-level encryption addresses threats at the chip-reader interface, but data protection must extend across the entire system infrastructure—from table readers through local processing units, network connections, central servers, and integration endpoints:
Reader-to-processor communication: Data transmitted between table readers and their associated processing units travels across wired connections that may be physically accessible under table structures. Encryption protocols applied to these communication channels prevent interception by parties who might tap into cabling infrastructure. Leading systems use encrypted communication standards that authenticate both endpoints and protect data payloads.
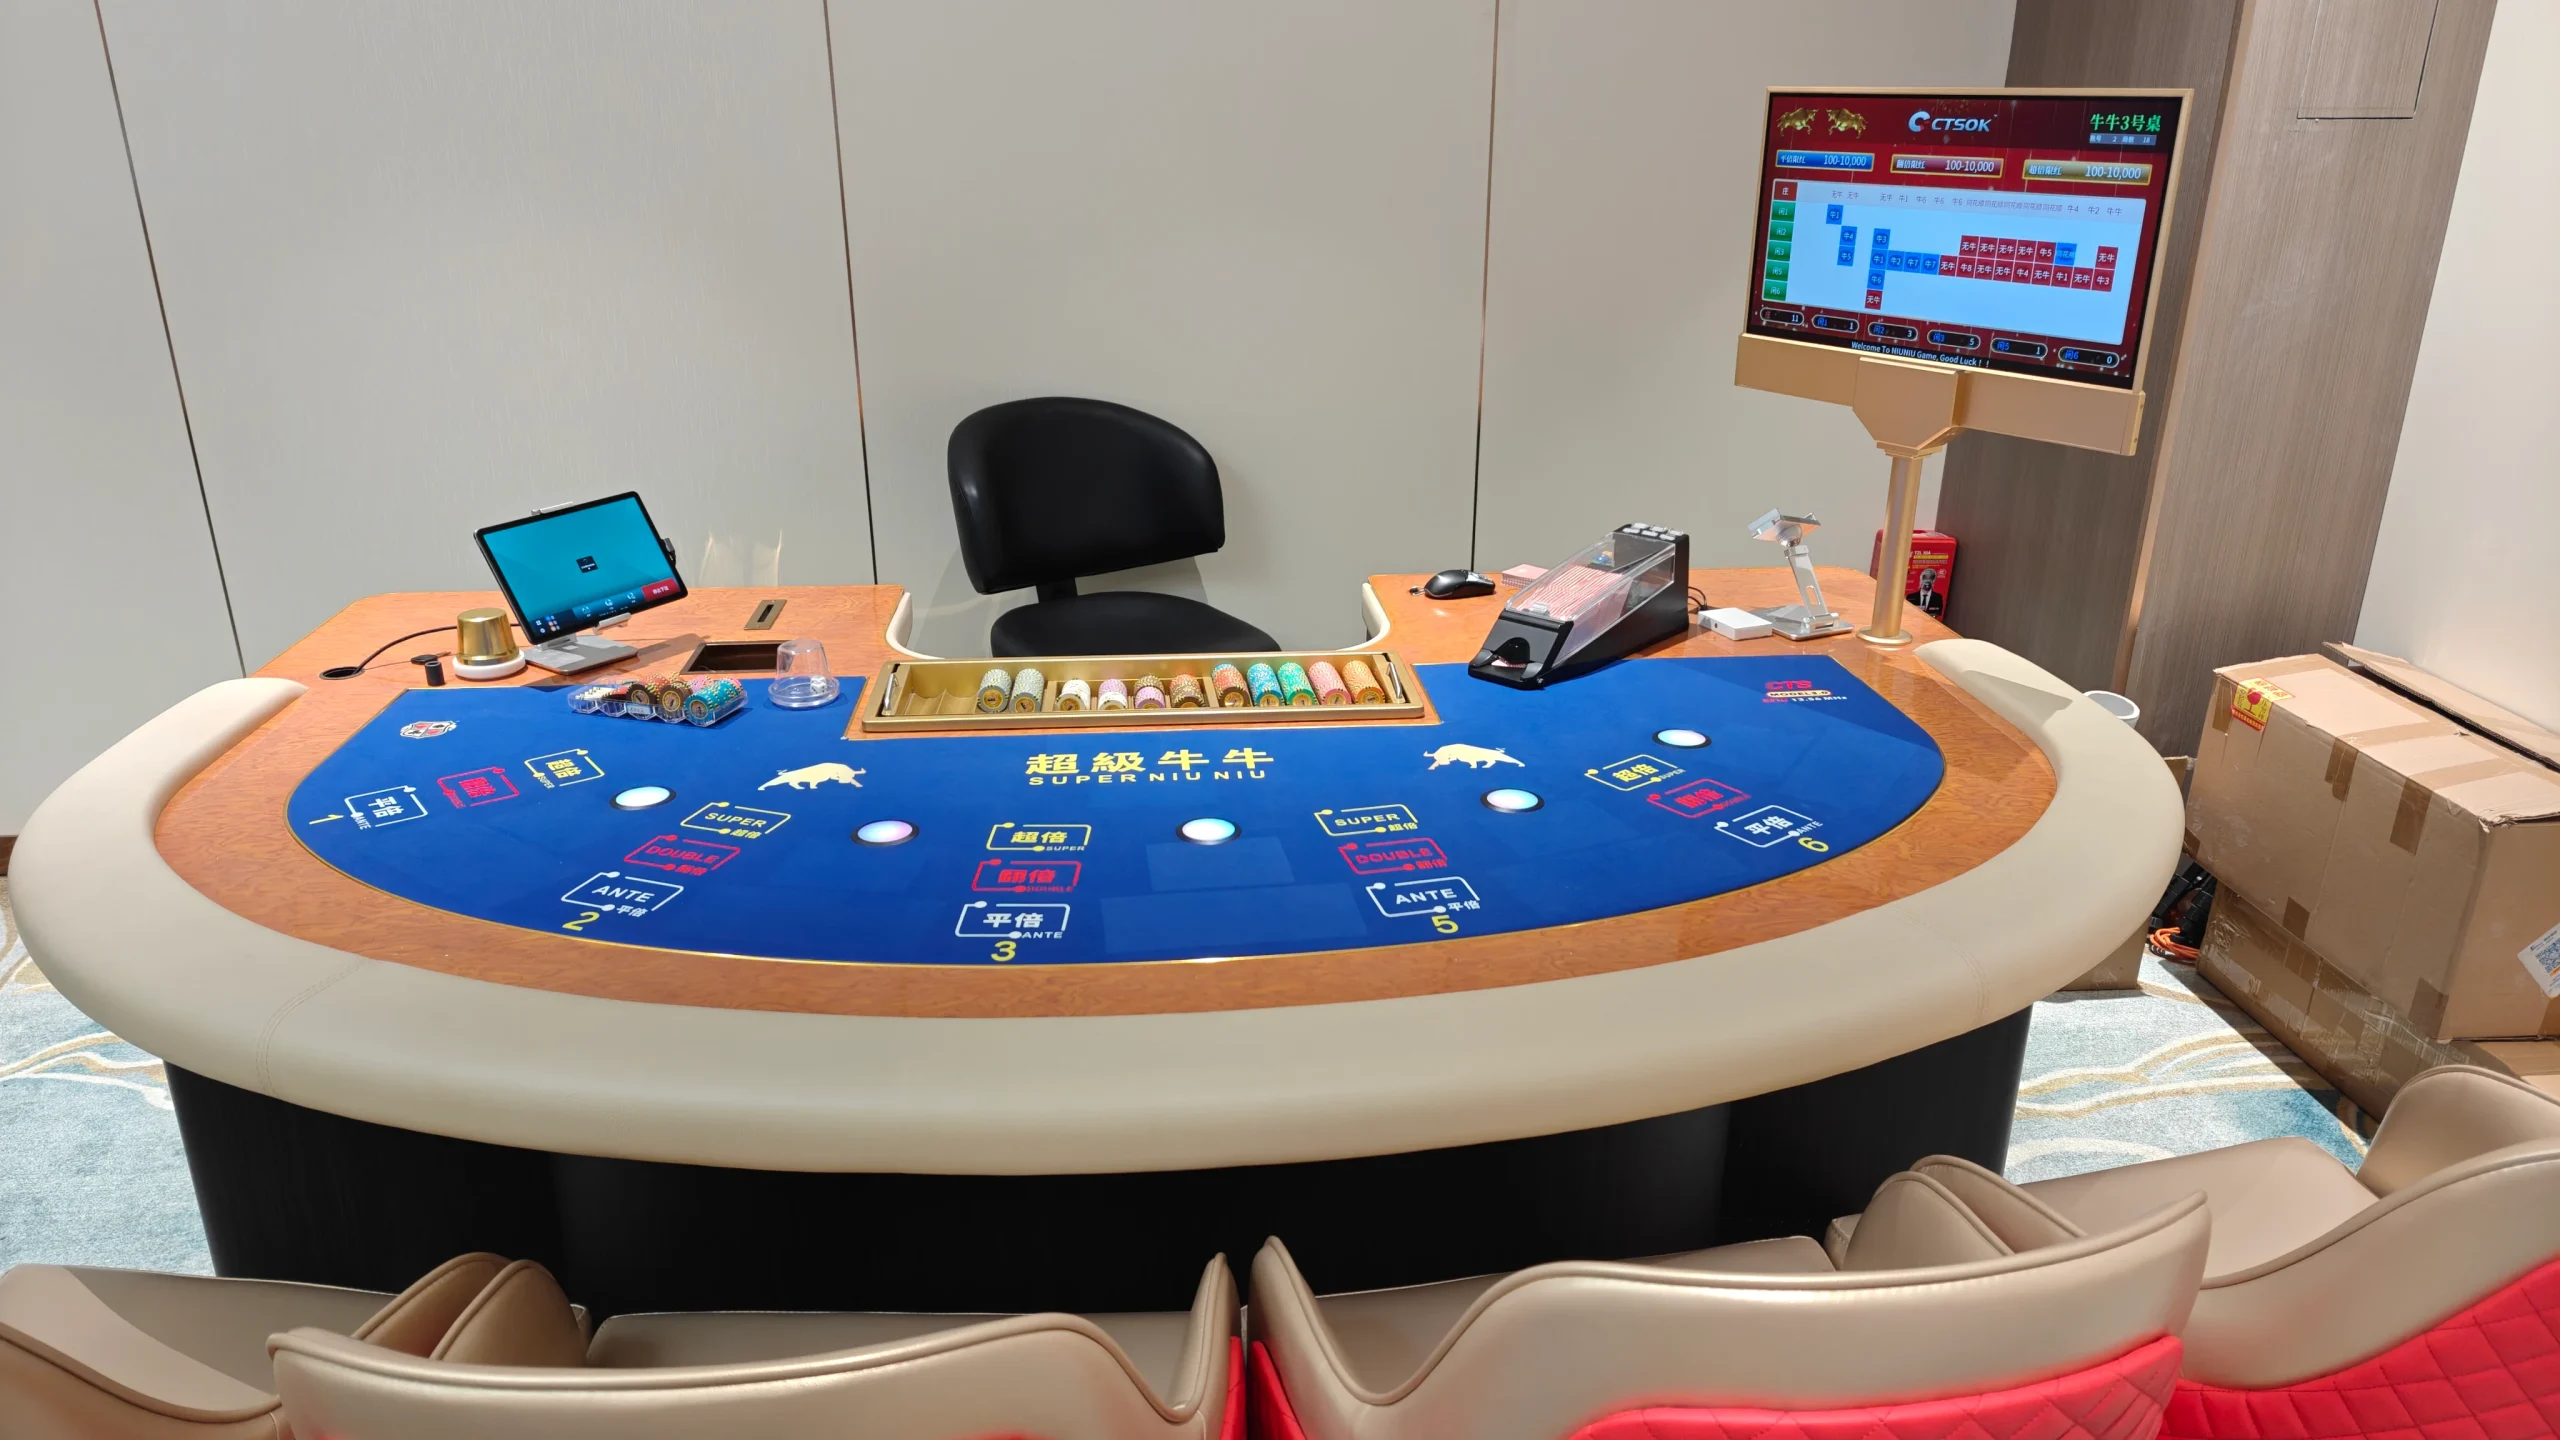
Network transport security: As RFID data flows from table-level processing units to central servers, it traverses the property’s network infrastructure. Transport layer encryption—similar to standards used in financial transaction networks—protects data against interception at network switches, routers, and other infrastructure points. Network security configurations should also include segmentation that isolates RFID data flows from general operational traffic, reducing the attack surface available to unauthorized parties.
Central server data protection: The central RFID database contains the complete chip inventory, including serial numbers, denomination mappings, issuance histories, and encryption key material. This database must be protected with access controls that limit query permissions to authorized system components, encryption at rest that prevents data exposure if storage media are compromised, and audit logging that records every access event for security review.
Integration endpoint security: When RFID data flows into downstream systems—table management applications, compliance reporting tools, financial reconciliation modules—each integration point must enforce its own security controls. API interfaces that connect RFID systems to downstream applications should require authentication, use encrypted connections, and validate data integrity to prevent injection attacks or data manipulation at integration boundaries.
Defense Against Specific Attack Vectors
RFID casino chip security must address several well-documented attack vectors that target different points in the system:
Cloning and Counterfeiting
Cloning attacks attempt to create chips that duplicate legitimate transponder data, producing counterfeit chips that pass standard read verification. Effective defenses include:
– Challenge-response authentication: As described above, dynamic challenge-response protocols prevent cloning because a cloned chip cannot generate correct responses to novel challenges without possessing the original chip’s secret key material RFID Baccarat Table.
– Unique per-chip key diversification: Even if an attacker extracts data from one chip, key diversification ensures that the extracted key material cannot be used to program counterfeit chips that would pass authentication with other chips’ keys.
– Physical tamper evidence: Transponder encapsulation within the chip body includes tamper-evident features that make attempts to extract the transponder for data harvesting visibly apparent, enabling detection during routine chip inspection.
Skimming and Eavesdropping
Skimming attacks use unauthorized readers to capture data from legitimate chips as they pass through detection zones. Eavesdropping attacks intercept communications between legitimate readers and chips. Defenses include:
– Mutual authentication: Chips that authenticate readers before responding prevent unauthorized readers from extracting data, even when the unauthorized reader is within signal range.
– Communication encryption: Session keys established during mutual authentication encrypt all subsequent data exchanges, making intercepted communications unintelligible to eavesdropping parties.
– Signal range management: Reader antenna calibration that limits the effective communication range to the immediate tray and transaction zones reduces the physical area where skimming devices could operate undetected. Chips outside the reader’s active zone do not respond to read requests, limiting exposure to nearby unauthorized readers.
Relay and Replay Attacks
Relay attacks use proxy devices to forward communications between a legitimate chip and a remote reader, allowing an unauthorized party to use a genuine chip’s authentication from a different location. Replay attacks capture legitimate chip responses and retransmit them later. Defenses include:
– Nonce-based challenge-response: Unique nonce values in each read event make replayed responses invalid, as the reader’s expected response changes with every new challenge.
– Time-based validation: Some implementations incorporate time constraints that limit the validity window for challenge-response exchanges, detecting relay attacks that introduce communication delays beyond normal parameters.
– Distance bounding protocols: Advanced systems may implement distance bounding techniques that verify the physical proximity of the chip to the reader, detecting relay attacks that extend the effective communication distance beyond the expected range.
Database and Infrastructure Attacks
Attacks targeting the system infrastructure—rather than individual chips—seek to manipulate chip records, alter denomination mappings, or extract encryption key material from central databases. Defenses include:
– Access control enforcement: Role-based access controls that restrict database operations to authorized system components, preventing unauthorized modifications even by personnel with general system access.
– Encryption key isolation: Master key material used for key diversification is stored in dedicated cryptographic hardware—hardware security modules—that prevent key extraction even by parties with database access privileges.
– Audit trail integrity: Every database operation is recorded in an immutable audit log, enabling retrospective detection of unauthorized changes and supporting forensic investigation if a breach is suspected.
Regulatory Compliance and Encryption Standards
Gaming regulators increasingly recognize that RFID chip security must meet defined standards, not merely rely on vendor claims of adequate protection. Compliance considerations include:
Encryption algorithm requirements: Some jurisdictions specify acceptable encryption algorithms for financial instrument protection, requiring that casino RFID implementations use algorithms recognized by international cryptographic standards bodies. Properties must confirm that their chosen encryption methods satisfy these regulatory requirements, which may exclude older algorithms that are no longer considered secure against current attack capabilities.
Key management standards: Regulatory frameworks may impose requirements on encryption key management practices, including key generation methods, key storage security, key rotation schedules, and key retirement procedures. These requirements ensure that encryption keys are managed with the same discipline applied to other financial security controls within the casino operation.
Data retention and auditability: Regulations that require detailed chip transaction records also imply requirements for data protection throughout the retention period. RFID transaction data must remain readable for compliance reporting while remaining protected against unauthorized access during storage. Encryption at rest and controlled access mechanisms must satisfy both requirements simultaneously.
Incident reporting obligations: When a security breach affects RFID chip data—whether a suspected cloning attempt, a database intrusion, or a communication interception event—regulatory frameworks may require prompt reporting to gaming authorities. Properties must define incident detection thresholds and reporting procedures that meet these obligations, including documentation standards that describe the nature and scope of detected events.
Cross-jurisdictional considerations: Properties that operate in multiple jurisdictions may face varying security standards that require different encryption configurations or data handling practices for different regulatory environments. System architecture must accommodate these variations, potentially maintaining separate configuration profiles that apply jurisdiction-specific security rules to the appropriate chip sets and operational areas Macaumr Casino Supplier.
Encryption Performance and Operational Impact
Encryption and authentication operations add processing time to every chip read event. In a live table environment where transactions occur rapidly, this processing overhead must remain within limits that do not disrupt game flow:
Read cycle timing: A complete read cycle—including challenge generation, chip response computation, reader verification, and data extraction—must complete within a timeframe that supports the table’s transaction pace. Leading implementations achieve read cycle times that are imperceptible to dealers and players, integrating seamlessly into normal chip handling rhythms.
Multi-chip read performance: Table readers must resolve multiple chips simultaneously, particularly during tray counts and bulk transaction verifications. The cryptographic processing load for simultaneous multi-chip authentication must be handled by the reader’s processing unit without creating delays that affect operational throughput. Reader hardware specifications should be evaluated against the maximum anticipated concurrent chip count at each table type.
System-wide processing capacity: During peak operational periods, the aggregate cryptographic processing load across all active tables must remain within the central system’s capacity. Performance monitoring during deployment testing should validate that peak-period authentication volumes do not create processing bottlenecks that slow read response times or delay alert generation.
Future Directions in RFID Casino Chip Encryption
The security landscape continues to evolve, and RFID chip encryption must advance to address emerging threats and leverage new cryptographic capabilities:
Stronger algorithm adoption: As computational power available to potential attackers increases, encryption algorithms must evolve to maintain adequate security margins. Future implementations will likely adopt algorithms with larger key sizes and more sophisticated structures that resist attacks leveraging advanced computing capabilities.
Post-quantum cryptography preparation: Although practical quantum computing capable of breaking current encryption remains speculative, forward-looking properties are beginning to evaluate post-quantum cryptographic algorithms that would remain secure even if quantum computing advances faster than expected. This preparation ensures that chip security can be upgraded proactively rather than reactively.
Enhanced mutual authentication: Future systems may expand mutual authentication to include additional verification layers, such as location confirmation through integrated positioning data or temporal validation through synchronized time stamps that detect relay attacks more reliably.
Blockchain-anchored audit trails: Some emerging approaches propose anchoring RFID transaction audit records in distributed ledger structures that provide immutable verification of data integrity, preventing retrospective manipulation of transaction logs even by parties with database access.
FAQ
What encryption algorithms are commonly used in casino RFID chips?
Leading implementations typically employ symmetric key algorithms recognized by international cryptographic standards organizations, combined with key diversification schemes that produce unique per-chip keys. Specific algorithm selection depends on regulatory requirements, processing constraints within the transponder, and the property’s security policy. Properties should verify that their chosen algorithms satisfy both current security standards and applicable regulatory mandates.
How does key diversification protect the entire chip set if one chip is compromised?
Key diversification uses a master secret and each chip’s unique serial number to compute an independent encryption key for that chip. Because the key derivation function is designed so that knowledge of one chip’s derived key does not reveal the master secret or any other chip’s derived key, a breach of one chip’s key material does not cascade to other chips in the inventory. The master secret remains protected within the system’s hardware security module, and the compromised chip’s key can be deactivated without affecting any other chip’s authentication capability.
Can unauthorized readers extract data from casino RFID chips?
Properly configured systems prevent unauthorized data extraction through mutual authentication protocols. Chips are designed to respond only to readers that successfully authenticate themselves as legitimate casino infrastructure components. Unauthorized readers that cannot present valid authentication credentials receive no response from the chips, blocking data extraction attempts. Additionally, communication encryption ensures that even if an unauthorized reader could somehow initiate a read, the transmitted data would be encrypted with session keys unavailable to the unauthorized device.
How are encryption keys managed and rotated in casino RFID systems?
Key management follows disciplined protocols similar to those used in financial security systems. Master key material is stored in dedicated hardware security modules that prevent extraction and enforce access controls. Key rotation schedules—whether triggered by time intervals, security events, or regulatory requirements—are executed through controlled procedures that update chip programming and reader configurations in coordinated sequences. Key retirement procedures deactivate old key material while maintaining continuity of chip authentication under new keys, avoiding operational disruption during transitions.
What happens when a chip fails authentication at a table reader?
When a chip’s authentication response does not match the expected value, the reader system generates an immediate alert to the floor supervisor and security monitoring. The chip is flagged as a potential counterfeit, compromised device, or malfunctioning transponder. Security personnel investigate the flagged chip, determining whether the authentication failure results from a technical issue (such as transponder damage from physical wear) or a genuine security concern requiring further action. The chip may be removed from circulation for detailed examination, and the incident is documented for regulatory reporting where applicable.
Are RFID chip encryption standards consistent across different jurisdictions?
Encryption standards are not universally consistent across jurisdictions. Different gaming authorities may specify different acceptable algorithms, key management requirements, and data protection practices. Properties operating in multiple jurisdictions must configure their RFID systems to comply with each applicable regulatory framework, potentially maintaining distinct security profiles for different operational areas. System architecture should support this configurability without requiring separate physical infrastructure for each jurisdiction.
Conclusion
RFID casino chip security depends on encryption standards and data protection protocols that address threats at every level—from the transponder embedded in each chip to the central database that manages the entire inventory. The layered architecture of modern casino RFID systems—combining transponder encryption, challenge-response authentication, mutual verification, infrastructure protection, and rigorous key management—provides a security framework robust enough for the financial instrument status that casino chips carry. Properties that understand and invest in these security dimensions position themselves not only to prevent losses from direct attacks but also to satisfy evolving regulatory expectations and maintain the trust that underpins their gaming operations. As attack methods advance and cryptographic standards evolve, ongoing attention to encryption quality and data protection rigor remains an imperative for every RFID-equipped casino floor.